Access Control Contracts Between MCP Servers and Supabase for Agent Workloads
Layered credentials, RLS, and MCP limits decide what agents can touch.
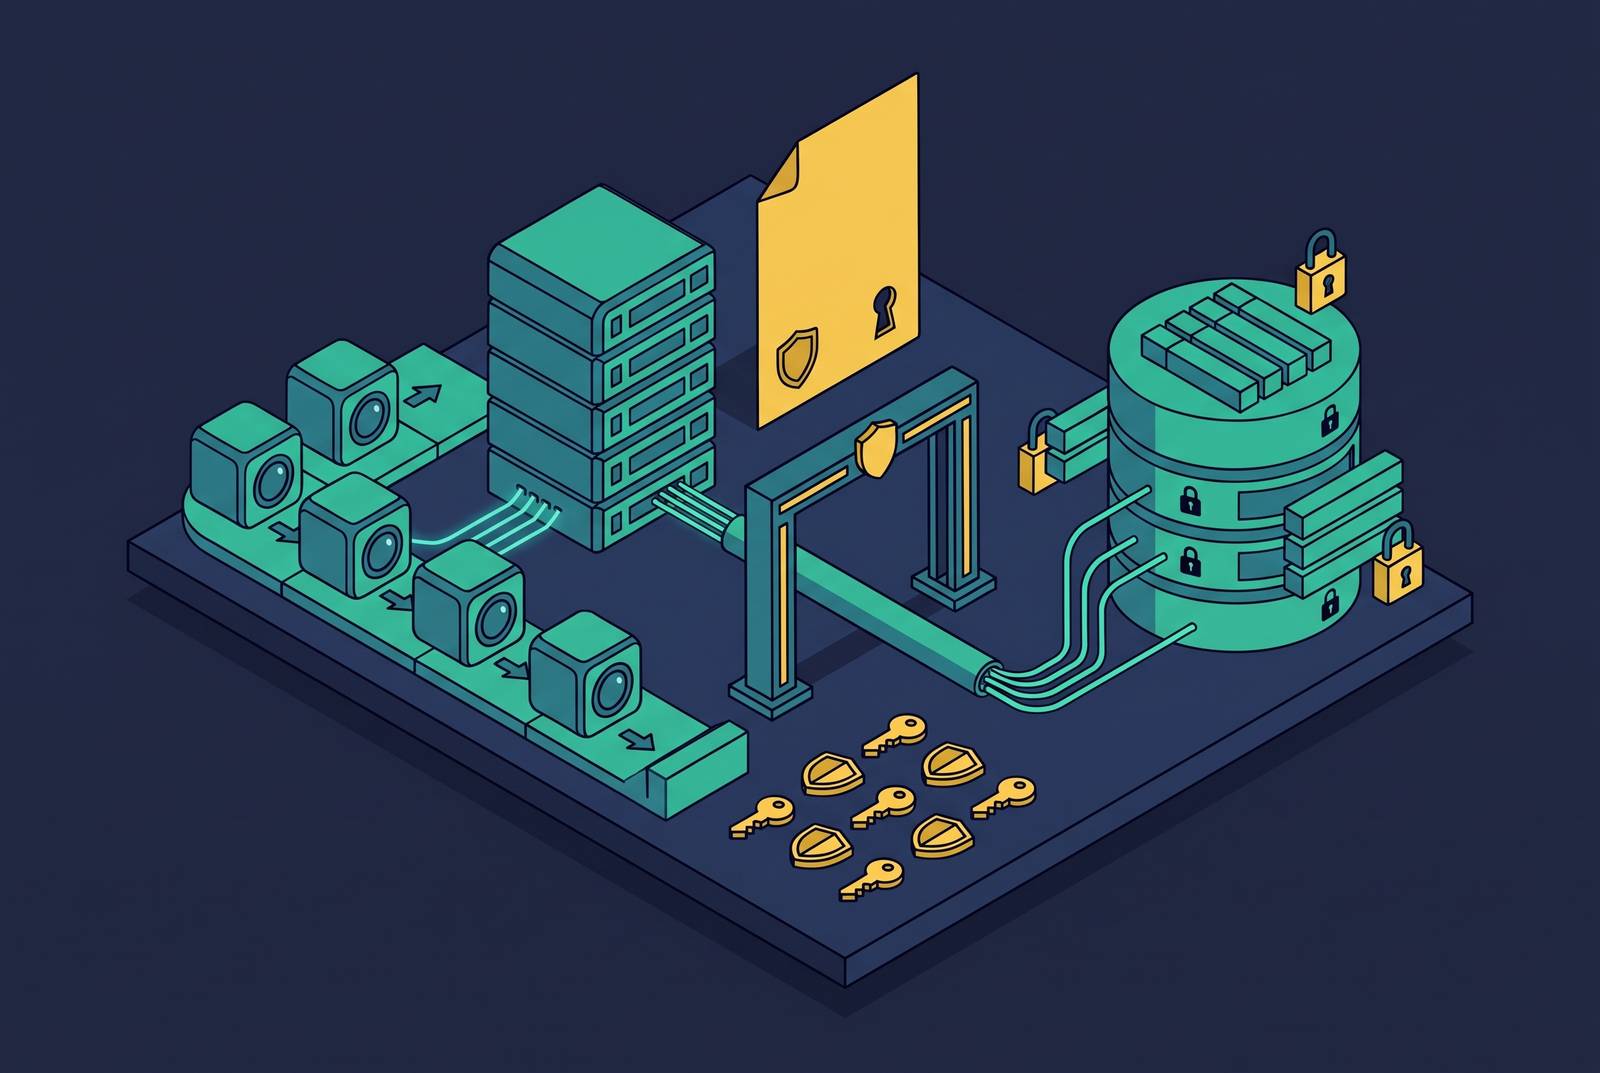
For governed data access on Supabase via MCP, use a per-app, per-user MCP server that passes the signed-in user’s auth context to queries governed by Row Level Security. For analytics, expose pre-modeled metrics through a dedicated, governed MCP tool, keeping production tables off-limits to direct agent access. The access control contract needs credentials, RLS, and MCP-layer enforcement to work together, with audit trails that show those boundaries hold.
Why the MCP-to-Supabase connection is not a single trust boundary but a layered contract
The application data plane and the development control plane act on behalf of different principals. The Supabase-announced app MCP server runs inside the developer’s own project and authenticates as the signed-in user. The official Supabase MCP server instead gives development assistants access to management operations and SQL execution. These are not interchangeable routes to the same permissions. Putting the control-plane server into a user-facing workflow removes the end-user RLS boundary that the application depends on.
The distinction becomes clearer at the database interface. The Data API plus Row Level Security reads and writes application rows on behalf of an end user, while the official MCP server and the Management API operate on the control plane. Authenticating a user at the front of a workflow is insufficient if a later tool executes with a different principal.
That creates at least three independently breakable layers. The credential determines the authority available to the agent, RLS determines which rows that authority permits, and MCP enforcement determines which operations the agent can invoke. A restriction at one layer does not establish a restriction at another. For example, limiting tool exposure does not prove that a permitted SQL tool evaluates end-user policies.
What each credential type actually grants and where RLS fits in
The choice between a service role key and an anon key has the largest blast radius because the service role key bypasses all RLS policies. It provides unrestricted access to the database. RLS cannot constrain a credential that bypasses it. The service role key is appropriate for schema migrations, administrative tasks, and internal tooling.
That authority also makes discovery unusually consequential. With unrestricted SQL access, the auth schema is one query away, while list_tables and column introspection give the agent a map of the database. Discovery shows an already privileged agent the structure available under its existing permissions, making sensitive data easier to find. A detailed set of RLS policies offers no protection along this bypass path.
For data operations, the default should therefore be the anon key, with the service role key reserved for migrations and administrative work. The anon key operates within RLS, while the signed-in user’s auth context supplies the identity needed for per-user access. The app MCP server announced at Supabase Select is built to preserve that context with every query. These are distinct parts of the contract. An audit trail must make the agent and its session identifiable so that the authority used for agent activity can be examined.
Where the MCP layer itself fails to enforce what credentials and RLS promise
Correct database permissions do not resolve authorization gaps in the MCP interface. The hosted server has no fine-grained OAuth scopes yet, so an OAuth app receives write access to everything rather than permission for a selected subset of tools. Scoped personal access tokens allow per-tool permission restrictions for a given agent session. Choosing OAuth does not establish the same tool boundary available through a scoped PAT.
The execute_sql tool introduces a separate identity gap because it runs under the developer connection. It does not check RLS for each end user. Write and migration tools can also INSERT, UPDATE, DELETE, and alter schema, allowing a confused or compromised agent to modify or destroy regulated data.
Prompt injection adds a failure surface even when a tool performs its intended operation. Returned rows can contain untrusted instructions, and prompt wrapping is not a complete security boundary. The “lethal-trifecta” pattern combines private-data access, exposure to untrusted content, and the ability to communicate externally. Read access can therefore support an exfiltration attack. Traditional DLP at the network edge, on file shares, or inside SaaS-native rule engines is outside the MCP tool path, so the tools already in place to inspect traffic miss those calls.
The scoping controls that exist today and what each one actually reduces
Teams should apply the available controls cumulatively, beginning with the broad removal of mutation authority. The read_only flag demotes the agent to a read-only Postgres user, eliminating write and migration risk. It does not restrict which rows remain readable.
Next, project_ref pinning confines the session to one project instead of allowing an account-wide credential to reach all of a team’s projects. Feature-group selection narrows the exposed tool surface within that scope. A task can have database read tools without also getting Edge Function deployment tools. Even with project pinning and tool selection, a developer connection does not run as an application user.
For user-facing workloads, the per-app, per-user MCP pattern ties access to the user. The agent authenticates as the signed-in user, and RLS decides which rows that user can reach. The team also owns the exposed tools. Sensitive workflows, including payments, admin actions, and third-party API calls, should go through backend code or Edge Functions. This keeps those operations out of a general SQL interface.
Supabase’s configurable rate limits apply to authentication endpoints, with limits scoped to projects and IP addresses. The Data API has no built-in per-key rate limiting. A narrowly authorized agent can still issue unbounded queries, so least privilege alone does not bound database work or cost.
Why analytics queries are a distinct risk surface and what a governed data layer changes
Analytics joins three risks that access controls alone cannot resolve. An agent can bypass RLS with the wrong credential, scan unbounded rows, and invent metric logic from raw table structure. Even an authorized read can be operationally expensive. Unbounded scans against production Postgres degrade performance for application users, while a plausible calculation can produce a metric that does not reflect the business definition.
Expensive reporting workloads should therefore move to replicas, materialized views, or external analytics systems. A governed data layer goes further by pre-calculating metrics and modeling them into datasets behind a stable interface, such as DuckDB over Parquet. The agent consumes a defined result rather than constructing an ad-hoc calculation against production tables. This separates calculation authority from conversational interpretation. It removes the specific source of metric hallucination created by guessed calculation logic and takes agent-issued analytics load off production.
A dedicated data-analysis MCP server can expose list_tables, get_metric, and later run_sql under one governed tool contract. The recommended starting surface is read-only metadata and one KPI tool, giving the agent useful context without broad SQL access. Semantic context is part of the boundary. Constraining an agent to selected data sources without explaining their business meaning leaves it without the context needed for reliable analytical tasks.
Governance must consequently live inside this access layer, with read-only enforcement, role-based access control, and audit trails built in from the start. Moving data away from production does not put those controls in place by itself. Nor does a stable interface set who can query each dataset. The governed layer combines defined calculations with access restrictions so that analytical correctness and authorization are handled together.
Which MCP server should connect an agent to Supabase with row-level access controls
If the agent acts for a signed-in user in a production application, the appropriate path is the app MCP server. The user authenticates normally, the user’s auth context travels with queries, and RLS restricts the rows the agent can reach. The team owns the server code and chooses the tools it exposes. This is the application-access branch of the decision. It is not a development assistant repurposed as a production authorization layer.
That setup requires asymmetric signing keys and the Supabase Auth OAuth server to be enabled. One shadcn command adds an authenticated Edge Function to the codebase, ready for deployment to Supabase. The deployment mechanism does not replace the permission design. Its value is that the authenticated server lives inside the project, where the team can control its tool contract while retaining the user’s RLS boundary.
If the job is instead build-time work on schemas, migrations, Edge Functions, or project configuration, the official control-plane MCP server is the intended path. It serves coding assistants such as Cursor, Claude Code, and Windsurf. Supabase explicitly scopes this server to development. Development access still needs constraints. Teams should apply read_only, project_ref pinning, and feature-group selection to narrow the capabilities available for the task.
If the agent runs headless or on a schedule, or needs narrower OAuth scopes and per-user revocation, direct Management API access is another path. Key rotation, domain setup, and org-level governance require it where those operations exist only there. The trade-off is losing the MCP layer’s cross-agent observability, shared rate limiting, and ability to change tool versions without redeploying agents. This remains a control-plane choice.
If the workload is analytics, none of those three surfaces is the right primary query path. The governed data layer should expose pre-modeled metrics through a dedicated MCP tool, with production Postgres off-limits to agent-issued analytical queries. The decision turns on the agent’s job.
Observability as the enforcement mechanism that makes the contract auditable over time
The architectural choice establishes intended authority, but observability shows whether agent activity remains within it. Credential misuse, unbounded scans, and RLS bypass can appear in logs before they become breaches, provided the relevant signals are being watched. Agent-initiated change logs should capture actor type, whether human, agent, or system, together with the agent identifier, which API key or MCP session was involved, the change type, and rollback availability.
Database metrics need to be consolidated with application-layer observability to reveal failures that cross those boundaries. A latency spike cannot be understood fully without its relationship to connection saturation, just as query performance needs the context of deployment events. Agent traffic needs its own operational view. Slow queries, unbounded scans, and connection saturation should raise alerts before they affect application users, so they stand out from the rest of the application’s queries.
At the MCP level, teams should track daily tool-call volume, success rate by tool, validation errors, permission errors, timeouts, and median and slow-tail latency. These signals describe how the service behaves, while value needs separate measurement through completed agent tasks and deflected requests that users can now answer without the analytics team. Popularity is not a health signal. In the registered-server ecosystem, three of the four metrics that predict server growth are external discoverability signals.
For governed analytics, the decisive audit record identifies which agent queried which metric and when. That record shows agents’ use of the defined source of truth or a return to metric proliferation through a new interface. A governed dataset without usage visibility leaves that question unanswered. Trust in the access control contract is earned through observable agent behavior over time.