Failure Modes When AI Agents Bypass the MCP Layer and Reach Supabase Directly
Direct Supabase access invites resets, leaks, and outages.
Tomás Wierzbicki
Section
15 stories in Agent-Safe Data Access.
Direct Supabase access invites resets, leaks, and outages.
Certified datasets and read-only MCP access replace raw SQL.
Agents should query governed analytical copies, never production Postgres.
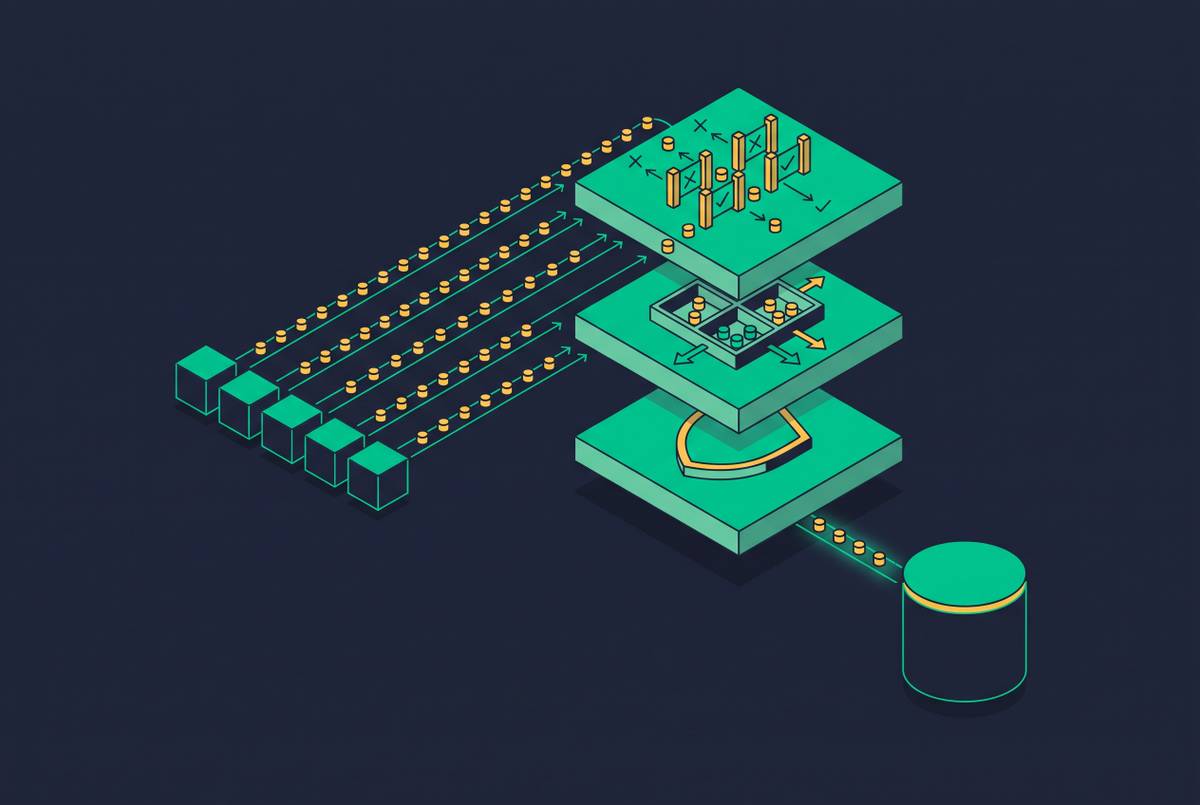
Four database layers must work together to safely govern AI agent access to production Supabase.
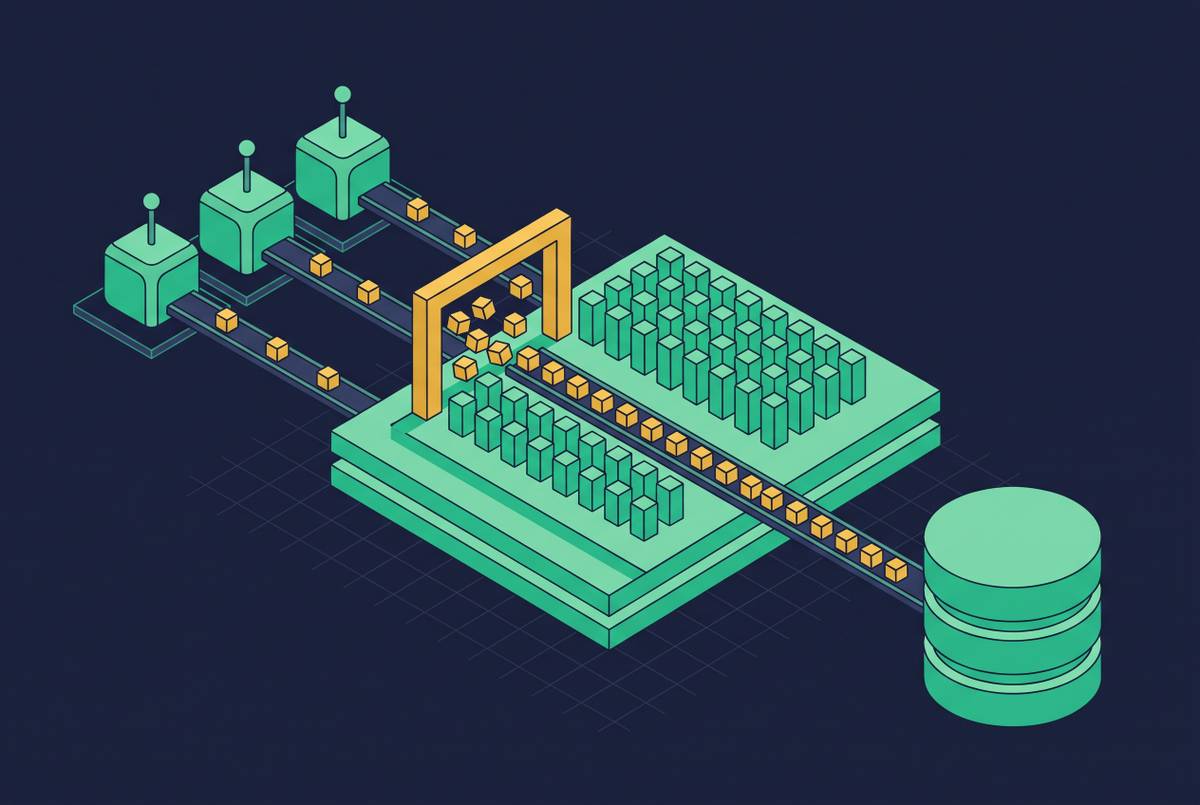
Agents should query pre-modeled metrics through MCP, not raw Postgres.
How you shape agent credentials determines what damage a compromised AI can inflict.
Agents get approved metric views and scoped roles, not tables.
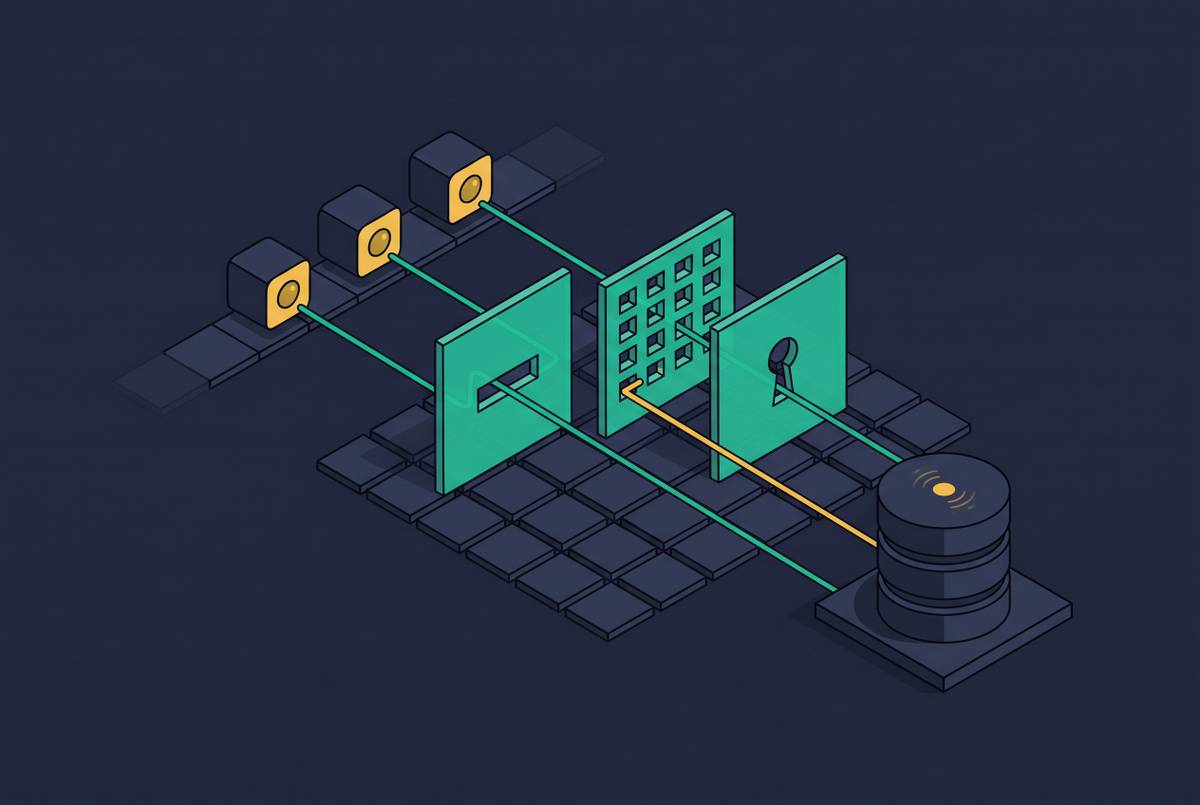
Layered credentials, RLS, and MCP limits decide what agents can touch.
Why AI agents should query governed datasets, not production Supabase.
Server logs show what ran, but audit trails must show why.
Agents should query modeled metrics, never raw databases.
Poisoned database records can hijack agents because models can't separate data from instructions.
Supabase's RLS assumes a human at the keyboard, and AI agents break that.
Read-only roles block writes, but only governed datasets limit what agents read.
Agents bring excess permissions, risky queries, and no audit trail.