Governed Metric Promotion Pipelines That Keep AI Agents Away From Raw Supabase State
Certified datasets and read-only MCP access replace raw SQL.
To let AI agents query Supabase data without direct database access, turn raw Postgres state into certified, pre-calculated datasets and make them available through read-only MCP Resources and Tools. A governed metric promotion pipeline builds trust into the infrastructure by enforcing versioned definitions, approval gates, and access policies before agents use the data.
Why raw Supabase access is the wrong default for AI agents
An agent writes SQL, runs it against Supabase, and returns a polished answer. This looks like a step toward self-service analytics. Yet syntactically valid SQL establishes nothing about the correct join path, fiscal calendar, reporting time zone, or definition of revenue. Without an agreed business model, each prompt asks the agent to reconstruct those decisions. The missing component is a governed interpretation layer.
Cube’s 2026 guide calls this failure “metric-definition drift.” The same question about last quarter’s revenue can yield three different numbers in three sessions because the calculation changes even though the SQL is still valid. More prompt examples do not make those definitions enforceable. A query that looks correct also gives no assurance that it leaves out another tenant’s rows. InfiniSynapse’s governance guide describes this risk as “prompt text widening a join.”
On Supabase, these semantic and security gaps also create operational costs. Production Postgres serves the application within connection-pool limits and OLTP compute that is not sized for analytical load. Agent queries compete for those resources. A read replica moves that load but uses the primary’s compute size, bills separately without plan compute credits, and adds disk at a premium over the primary. It can roughly double database spending without establishing which answers are approved.
What a governed metric promotion pipeline actually does
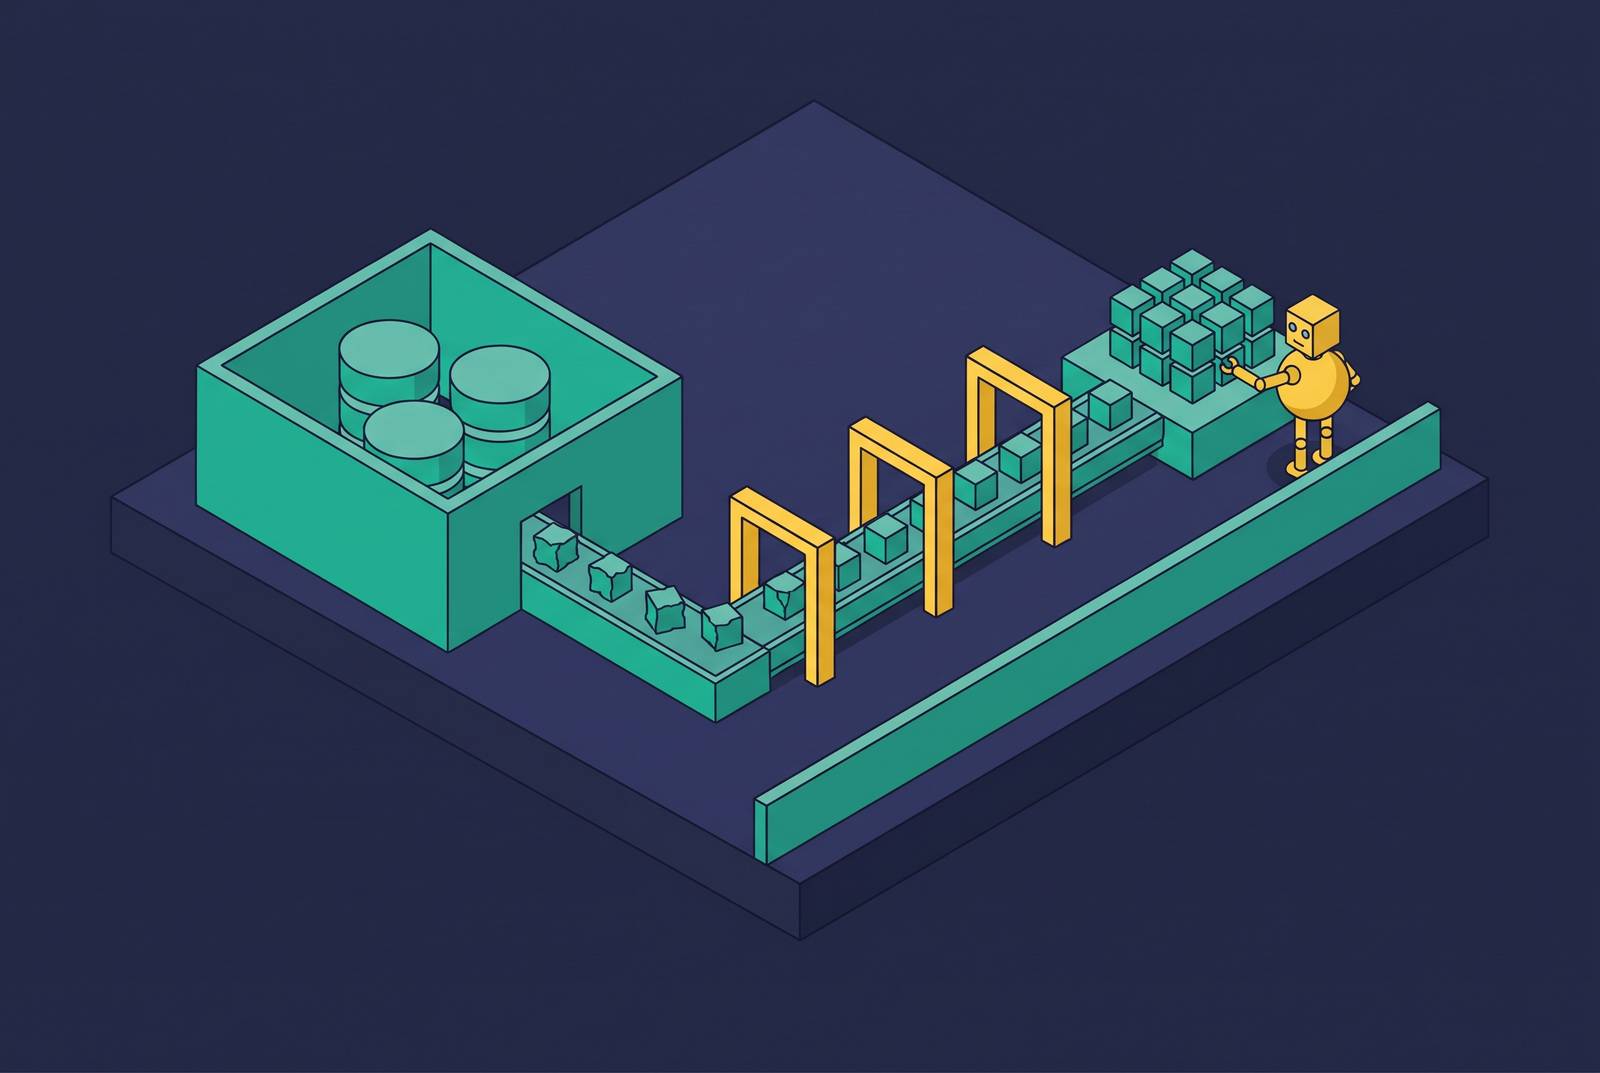
A governed metric promotion pipeline transforms raw Supabase Postgres data through successive modeling and approval stages into certified datasets. Each gate enforces requirements such as a versioned definition, approval record, lineage trace, or access policy compiled into the query.
This separates access from understanding of the business. Text-to-SQL translates a question into a query against available tables, while a semantic layer encodes the business meaning those queries must preserve. Cube’s guide states the distinction directly, explaining that “access without an agreed model of the business means every answer is re-derived from first principles.” Under governed access, the agent selects certified logic.
The design has three main parts: promotion stages, metric contracts, and read-only agent access surfaces. Stages transform data, contracts define what qualifies for approval, and access surfaces constrain consumption. In this design, governed Parquet datasets provide the analytical copy, queryable through DuckDB. Agents discover and request named datasets through MCP.
The promotion stages: how raw Supabase state becomes a certified dataset
The raw ingestion boundary establishes where data leaves production under controlled conditions. Supabase remains the source of record, separate from the agent’s analytical surface. This distinction addresses the resource contention created by direct access. Instrumentation begins here because ingestion still consumes production resources, even when downstream analysis does not.
Modeling then turns raw tables into structures with explicit grain, join paths, time behavior, and metric logic. Revenue acquires a definition that survives a new prompt. The semantic layer applies that definition at query time, while the policy layer enforces security and masking. Cube’s governed AI data access article describes the intended interaction as selecting approved metrics and dimensions by name instead of generating unrestricted SQL against every table.
Certification gives the modeled dataset a version, status, and approval record after review against its metric contract. Access rules take effect before query execution. Tenant, role, and region are incorporated into the SQL generated by the semantic layer, rather than checked after forbidden rows have already been returned. When the source data flow changes, re-certification must wait for lineage analysis, quality checks, and a review of the agent workflows that the change affects.
Governed exposure materializes certified data into Parquet files queryable through DuckDB and available as named MCP Resources. Agents receive an approved analytical surface. They therefore have no production table names from which to improvise joins and no query path to unapproved source tables.
Metric contracts: the versioned definitions that make promotion gates enforceable
A metric contract gives certification an enforceable meaning. It is machine-readable. Its identity fields include the metric name, version, status, and owner, with status expressed as draft, approved, or deprecated. Calculation fields specify the measure, aggregation method, allowed dimensions, filters, and time behavior, including fiscal calendar, timezone, and accumulation logic.
Lineage fields list the upstream tables and transformation steps, while governance fields hold the classification, consumer tiers, and approval with an effective date. Those dates anchor the versioned bindings agents compile against. Metric councils should publish effective dates. A changed definition can otherwise break workflows that depend on the previous version.
The access policy matrix uses those contracts to set the default permissions. Company-level KPIs such as total ARR and total pipeline receive broad access with source citations, while team-level metrics such as regional pipeline and support SLA use role-based access by function. Access to account-level metrics such as customer ARR and renewal risk must be restricted and logged. Finance-sensitive metrics, including margin and recognized revenue, need approved roles and must go through review. Experimental metrics are available to a limited beta group and must have a clear warning label.
For small teams, maintaining contracts can look like documentation overhead. The alternative cost is harder to detect. Marketing, finance, and product can get different answers for active customers until an investor asks for audited numbers. A strict data dictionary also prevents competing implementations such as SUM(revenue) and SUM(amount_captured) from silently becoming rival definitions of Q2 revenue.
The five agent access layers and why governing only the database layer leaves gaps
Database permissions cannot govern the entire agent interaction. The user layer establishes who is asking through role, team, and account scope. The agent layer separately identifies which approved agent is acting, its environment, and its owner. A read-only summarization agent belongs in a different control tier from an agent authorized to update records.
The tool layer limits what that agent may invoke through an MCP server allowlist and SQL tool scope. An analysis agent does not acquire write access because an incident bot needs it elsewhere. The metric layer restricts available definitions to approved semantic metrics with known versions and owner status. The answer layer controls what may be shown through aggregation thresholds, citation requirements, and review policies for finance-sensitive outputs.
Multi-agent architectures require centralized identity and policy enforcement. Agents are separate versioned services in a registry with defined capabilities, tool entitlements, and constraints, rather than processes inheriting standing credentials. Bain’s agentic platform architecture identifies built-in access controls, identity propagation for non-human principals, and audit tooling as foundations for accountability.
The replay log provides evidence that those controls operated. It records the policy version, SQL, and egress check. InfiniSynapse’s guide states that “without those three, the query was allowed; it was not governed.” Exceptional access also needs explicit boundaries, with just-in-time, expiring break-glass access, no production credentials for dev agents, and synthetic data during prompt tuning.
Where MCP fits when connecting AI agents to Supabase without direct database access
MCP provides the exposure standard. It replaces N×M application-to-source connectors with N+M implementations of a common protocol. Servers expose Tools for actions, Resources for context, and Prompts for reusable analytical workflows. In this architecture, Resources make certified datasets discoverable by name without revealing the underlying production schema.
That distinction determines what an MCP server must expose. A server connected to raw tables does not become a governed metric service merely because it supports the protocol. The pipeline must apply the policy before the data reaches the MCP layer. Row-level control, certified definitions, and a replayable access record belong to the governed query path.
The U.S. National Security Agency’s May 2026 report stated that MCP’s rapid proliferation had outpaced development of its security model. MCP security guidance documents confused-deputy risks in proxy servers and forbids token passthrough. These limits reinforce the need for independent access enforcement. MCP remains useful precisely because its connection role is distinct from that enforcement.
MCP maintainers finalized a major revision on July 28, 2026, removing protocol-level session tracking. Client identity and capabilities travel in a _meta parameter with each request. For governed pipelines, this stateless protocol model reinforces the case for including policy version, tenant, and role in the request itself.
Running this on Supabase: the observability and isolation practices that make the pipeline viable in production
Production viability depends on measuring ingestion and isolating analysis. pg_stat_statements, enabled by default on most managed Postgres, records query mean and total execution time and call count. In PG13+, the timing fields are mean_exec_time and total_exec_time. These signals expose the cost of queries crossing the ingestion boundary rather than leaving source extraction as an unmeasured dependency.
Realtime Prometheus metrics and structured logging complete the minimum observability stack. Dashboards need p50/p95 latency to support scaling decisions. Together, these instruments connect upstream query behavior to the datasets the pipeline promotes. A metric cannot be traced reliably when the behavior of its source queries has never been measured.
Isolation routes analytical and agent traffic to the pre-modeled Parquet copy behind MCP. DuckDB is the analytical query engine, so these queries need no production connections. This removes agent-driven connection contention by design, while leaving ingestion as a production workload that still needs care. In particular, evaluating auth.uid() for each row in row-level access policies can slow scans of large tables, while wrapping it as a scalar subquery lets it be evaluated once.
The ingestion boundary must therefore preserve application latency as well as access rules. Any Supabase source schema change should trigger lineage analysis and quality checks before re-certification. That gate prevents structural changes from silently invalidating datasets that still appear approved.
What teams get wrong when they build this incrementally versus as designed infrastructure
User and database controls are implemented first, while agent authority and answer policies wait. By the time those gaps become visible, agents may already depend on inconsistent definitions. An investor, board member, or competing internal report then exposes the disagreement that the pipeline failed to detect.
The resulting conflict is organizational as well as technical. When sales, finance, and product each keep their own version of ARR, leaders debate the numbers, displacing discussion of what to do. Experimental metrics create a related failure when they share an MCP surface with certified metrics but lack warning labels or approved-role restrictions. An unfinished definition can look authoritative just because agents can access it.
Bain’s architecture states that “legacy enterprise AI platforms are structurally mismatched for agentic systems.” Role sessions built for people lack the contextual, least-privilege permissions that autonomous agents need for every tool call. Its argument for embedding security and governance by design follows from that mismatch.
The practical counter-pattern is to treat the pipeline as the product and agents as its consumers. A team taking this approach should start with the KPIs reconciled on the CEO dashboard and certify them through every promotion gate. A small, complete contract is preferable to broad but partial coverage. Expansion then builds on an established approval path.
How a governed data layer serves both human teammates and AI agents from a single surface
The certified dataset is useful beyond the agent workflow. It can power live dashboards, scheduled Slack or email summaries, and reconciliation of ARR to the billing system. Human teammates and agents use the same pre-calculated numbers without needing a dedicated data team or a separate data warehouse. The shared surface removes the need for each interface to maintain its own business logic.
Pre-calculation also changes how people receive those numbers. Scheduled delivery to inbox, Slack, or mobile replaces reliance on someone remembering to open a dashboard, and agents can consume the same push without additional infrastructure. This is headless analytics in practical terms, with governed data accessible through MCP or API. Trust rests on the approved dataset and its access path.